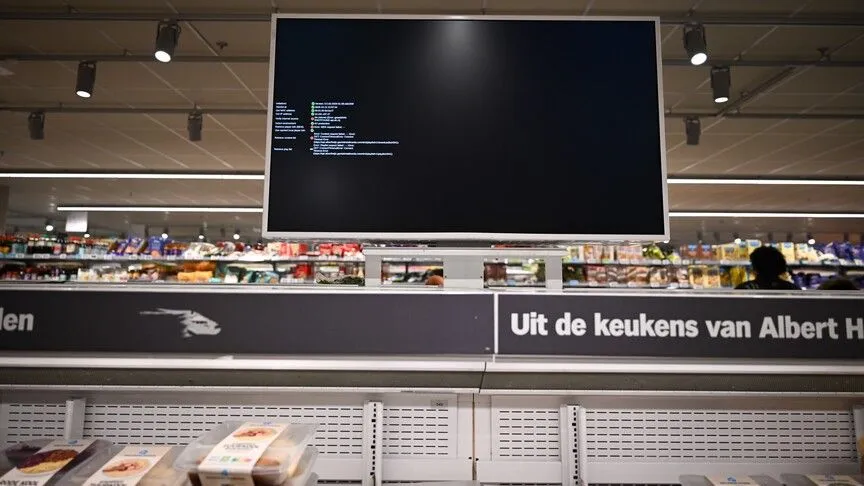
法国多家超市的制冷系统遭黑客攻击,导致荷兰食品配送出现中断。网络安全工程师凯文·泰利耶指出,老旧的制冷设备以及缺乏防护的管理系统极易使超市成为攻击目标。虽然能引发物理后果的网络攻击仍属罕见,但专家拉夫·皮林警告称,各系统间的互联互通可能会放大此类攻击的影响。通常情况下,超市货架空空如也意味着人们正在抢购物资,或是出现了供应中断的情况。而此次制冷系统遭攻击则是一个不太为人所察觉的诱因。
Refrigeration systems at French supermarkets hacked, cyber incident disrupts distribution in the Netherlands Cybersecurity engineer Kevin Tellier says outdated refrigeration equipment, exposed management systems can leave supermarkets vulnerable to attacks Cyberattacks with direct physical consequences remain relatively rare, but expert Rafe Pilling warns that interconnected systems can magnify impact Empty supermarket shelves usually suggest a shopping frenzy, panic buying ahead of a disaster or a disruption to deliveries. A cyberattack on refrigeration systems is a far less obvious explanation. Yet that is what happened in France, where refrigerated shelves were left empty after hackers targeted systems used by several major supermarket chains.
事实上,法国就发生了此类事件:黑客攻击了多家大型连锁超市的制冷系统,致使大量冷藏货架上的食品全部变质。攻击过程中,黑客远程操控系统,启动除霜功能使内部温度升至约50摄氏度(122华氏度),从而危及生鲜及冷冻食品的储存安全。此次遭攻击的制冷设备分别由丹麦丹佛斯公司、美国谷轮公司以及意大利迪克塞尔公司生产。
During the attack, hackers remotely manipulated the systems, using their defrost function to raise temperatures to around 50C (122F), threatening fresh and frozen food stocks. Systems from Danish manufacturer Danfoss, as well as those from US company Copeland and Italian company Dixell, were targeted.
受影响的超市纷纷将设备从网络中断开,此次事件也引发了人们对食品损耗及超市运营受阻的担忧。法国经济部长罗兰·莱斯库尔周二在议会透露,约有700个食品配送中心受到影响,初步估计遭攻击的超市数量则接近500家。
Affected stores disconnected their equipment from the network, while the incident raised concerns over potential food losses and disruption to supermarket operations. French Economy Minister Roland Lescure told parliament Tuesday that around 700 food distribution centers had been affected, while initial estimates put the number of targeted stores at around 500.
就在法国方面评估此次攻击的后果时,荷兰也传出了类似事件。该国最大的连锁超市阿尔伯特·海恩于周一宣布,由于在遭遇网络攻击企图后采取了“预防性”措施,多家配送中心已陷入停摆状态。尽管目前尚无证据表明这两起事件存在关联,但它们均凸显出网络攻击对超市维持食品保鲜及物流运转所依赖的基础设施造成的巨大冲击。
As France assessed the consequences of the attack, a separate incident was reported in the Netherlands. Albert Heijn, the country's largest supermarket chain, announced Monday that operations at several distribution centers had come to a standstill after systems were shut down "preventively" following an attempted cyberattack. While no link has been established between the two incidents, both highlight how cyberattacks can disrupt the infrastructure that supermarkets rely on to keep food fresh and supplies moving.
‘对法国食品供应链的攻击’法国合作超市集团U的负责人多米尼克·舍尔舍将这次制冷攻击描述为“前所未有、极其严重且不可接受的。”针对保鲜产品必需设施的攻击构成了“对法国食品供应链的攻击”,他在美国社交媒体平台上写道。该事件因对物理运营的直接影响而引起了网络安全专家的关注。
‘Attack on the French food supply chain’Dominique Schelcher, head of French supermarket group Cooperative U, described the refrigeration attack as “unprecedented, extremely serious and unacceptable.”Targeting equipment essential to preserving fresh products constituted “an attack on the French food supply chain,” he wrote on US social media platform The incident has drawn attention from cybersecurity specialists because of its direct impact on physical operations.
“这次是首批直接影响法国人日常生活的大规模网络攻击之一,”法国网络安全公司Synacktiv的网络安全工程师凯文·泰利耶对阿纳多卢通讯社表示。
"This is one of the first large-scale cyber-attack affecting directly the daily life of French people," Kevin Tellier, a cybersecurity engineer at French cybersecurity firm Synacktiv, told Anadolu.
网络安全公司Sophos的威胁情报高级总监拉菲·皮林表示,法国和荷兰的事件凸显了零售商面临的“两种不同但同样重要”的风险。
Rafe Pilling, senior director of threat intelligence at cybersecurity company Sophos, said the French and Dutch incidents illustrated "two different but equally important" risks facing retailers.
法国的攻击展示了“一次网络入侵如何导致直接的物理后果,扰乱制冷并毁坏库存,”他说。
The French attacks showed "how a cyber intrusion can have direct physical consequences, disrupting refrigeration and destroying stock," he said.
与此同时,荷兰事件展示了“一次网络安全事件如何干扰数字服务和业务运营。”“它们共同表明,零售业的网络风险如今已成为业务连续性问题,而不仅仅是IT问题,”皮林说。攻击是否可能变得更具破坏性?
The Dutch incident, meanwhile, demonstrated "how a cybersecurity event can disrupt digital services and business operations." "Together, they reinforce that cyber risk in retail is now a business continuity issue, not just an IT issue," Pilling said. Could attacks become more disruptive?
泰利耶表示,法国事件表明,即使没有特别复杂的方法,网络攻击也可能扰乱日常生活。
Tellier said the French incident demonstrated how a cyberattack could disrupt everyday life, even without particularly sophisticated methods.
“一个15岁的孩子都可能完成这次攻击,因为它并不十分复杂,”他说。
“A 15-year-old kid could have done this as it was not very sophisticated,” he said.
他还警告称,人工智能可能提升攻击者的能力,包括经验有限的攻击者。
He also warned that artificial intelligence could increase attackers' capabilities, including those with limited experience.
“我并不真的相信失控的人工智能情景……而是相信攻击者会利用人工智能来增强他们的潜力,”他指出。
“I don't really believe in rogue AI scenarios ... but rather in attackers using AI to augment their potential,” he noted.
皮林表示,法国事件并非个例,尽管具有直接物理后果的攻击在欧洲观察到的网络影响形式中并不占主导。
Pilling said the French incident was not an outlier, although attacks with direct physical consequences were not the dominant form of cyber impact observed across Europe.
“在欧洲,我们看到对运营技术和其他从未原本设计用于应对当前威胁格局的互联系统的立法和监管关注度正在增加,”他说。
“Across Europe we're seeing increased legislative and regulatory attention to operational technology and other connected systems that were never originally designed to face today's threat landscape,” he said.
“政府们认识到,这既是当前也是未来的一个重大韧性问题,”他补充道。
"Governments understand that this is a significant resilience issue both now and into the future," he added.
Pilling表示,使法国事件与众不同的是其现实后果的可见性。“故意跨越网络-物理阈值的攻击相对较少,”他说。
What made the French incident unusual was the visibility of its real-world consequences, Pilling said. “Attacks that deliberately cross that cyber-physical threshold are relatively rare," he said.
当被问及这些事件是否指向针对粮食安全的有意策略时,Pilling表示为时尚早,无法得出这样的结论。“我们尚未知道是谁负责或他们的动机是什么,”他说。
Asked whether the incidents pointed to a deliberate strategy of targeting food security, Pilling said it was too early to draw such a conclusion. “We do not yet know who was responsible or what their motive was,” he said.
食品供应链和零售运营有助于民众韧性,这意味着中断可能带来超出直接受影响公司的后果,他补充道。运营技术:被忽视的漏洞此类攻击可能产生超出数字世界后果的一个原因是其可能危及运营技术(OT),即用于监控和控制物理过程的硬件和软件,包括冷藏和工业机械。
Food supply chains and retail operations contribute to civilian resilience, meaning disruptions can have consequences beyond the companies directly affected, he added. Operational technology: The overlooked vulnerability One reason such attacks can have consequences beyond the digital world is their potential to compromise operational technology (OT), the hardware and software used to monitor and control physical processes, including refrigeration and industrial machinery.
“从我的技术角度来看,OT常被遗忘,在过去几十年里一直被严重低估,”Tellier说。
"From my technical perspective, OT is often forgotten and has been largely underestimated during the last decades," Tellier said.
OT系统设计为持续运行,这意味着更新和安全措施常被视为潜在的干扰源,他解释道。此类设备的多样性也可能使安全审计和改进变得困难。
OT systems are designed to operate continuously, meaning updates and security measures are often seen as potential sources of disruption, he explained. The diversity of such equipment can also make security audits and improvements difficult.
Tellier表示,这次袭击并未令其公司感到意外,该公司此前曾报告过影响丹佛斯冷藏系统及其他品牌的漏洞。
Tellier said the attack did not surprise his company, which had previously reported vulnerabilities affecting Danfoss refrigeration systems and other brands.
“我清楚地记得,三年前我的同事在报告丹佛斯漏洞时登录了控制面板,”他补充道。
“I remember well my colleagues logged on the control panel three years ago while they reported the vulnerability to Danfoss,” he added.
根据泰利尔的说法,丹佛斯与Synacktiv合作并在三个月后部署了补丁。然而,他表示,目前仍不清楚为何同一漏洞在2025年再次出现,并且今年在法国可能再次被利用。
According to Tellier, Danfoss cooperated with Synacktiv and deployed a patch after three months. However, he said it remained unclear why the same vulnerability appeared again in 2025 and could have been exploited in France again this year.
泰利尔说,丹佛斯曾将受影响的型号描述为过时且不再有资格获得安全更新,尽管其中一些仍在正常运行。
Tellier said Danfoss had described the affected models as obsolete and no longer eligible for security updates, although some were still functioning properly.
他还表示,更新OT设备也可能耗时较长,因为有些系统需要技术人员将U盘连接到每个设备上,手动安装更新。
Updating OT equipment can also be time-consuming, he said, because some systems require technicians to connect a USB stick to each device to install updates manually.
泰利尔还指出,可通过互联网访问的管理界面暴露在外,其风险本来可以通过安全审计被发现。
Tellier also pointed to management interfaces accessible through the internet, saying their exposure could have been identified through a security audit.
“直到今天,个别超市才意识到它们可能因网络攻击而蒙受损失,”他补充道。
“Individual Supermarkets were not aware until today that they could lose money on a cyberattack,” he added.
集中式系统,更广泛的后果 “集中式管理有助于降低成本,正是出于此目的才被实施。然而,集中化意味着引入必须定期审计的单点故障,”泰利尔说。
Centralized systems, wider consequences "Centralized management is useful to cut costs, it was implemented for this purpose. However, centralizing means introducing single points of failure that must be audited regularly," Tellier said.
皮林表示,现代超市依赖设备供应商、维护服务商、远程管理平台和联网设备。
Pilling said modern supermarkets rely on equipment vendors, maintenance providers, remote management platforms and connected equipment.
“这些依赖关系提高了效率,但如果生态系统中的安全管理不一致,也可能导致共享的故障点,”他说。
“Those dependencies improve efficiency, but they can also create shared points of failure if security isn't managed consistently across the ecosystem,” he said.
集中式管理软件使组织能够管理数千台设备,但如果中心平台被攻破,也可能放大攻击的影响,皮林解释道。
Centralized management software allows organizations to manage thousands of devices, but can also amplify the impact of an attack if a central platform is compromised, Pilling explained.
“提高运营效率的同一技术,也可能在安全事件发生时迅速放大其影响,”他说。
“The same technology that improves operational efficiency can rapidly magnify the impact of a security incident,” he said.
食品分销系统也可能成为攻击目标,以造成干扰,而无需直接攻击传统关键基础设施,如电力或水网络,他补充道。
Food distribution systems could also be targeted to cause disruption without directly attacking traditional critical infrastructure, such as power or water networks, he added.
“一次相对较小的技术妥协可能转化为库存变质、供应链中断和公众担忧,”皮林说。
“A relatively small technical compromise can translate into spoiled stock, supply-chain disruption and public concern,” Pilling said.
他还表示,此次事件也展示了对广泛部署的平台和共享服务发动攻击可能带来的后果。“这些系统越互联,一旦出问题,潜在影响就越大,”他说。新的“网络战场”根据Pilling的说法,防止类似攻击需要超市不仅关注软件更新,还要加强维持其运营的系统安全。
The incident also demonstrated the potential consequences of attacks on widely deployed platforms and shared services, he said. “The more interconnected these systems become, the greater the potential impact when something goes wrong,” he said. New ‘cyber battlefield’Preventing similar attacks will require supermarkets to look beyond software updates and strengthen the security of the systems that keep their operations running, according to Pilling.
“这既是一个韧性问题,也是一个补丁问题,”Pilling说。
“This is a resilience issue as much as a patching issue,” Pilling said.
他建议零售商识别其制冷系统,检查这些系统是否仍得到制造商的支持,并保护其远程访问接口。
He recommended that retailers identify their refrigeration systems, check whether they remain supported by manufacturers and secure their remote-access interfaces.
“如果远程访问在运营中是必要的,则应仅限于受信任的管理网络或受保护的远程访问服务,并配备强身份验证和适当的网络分段,”他说。
“Where remote access is operationally necessary, it should be limited to trusted management networks or secured remote-access services, with strong authentication and appropriate network segmentation,” he said.
Pilling还建议更新受支持的设备,隔离过时的控制器,并监控系统以发现意外变化。
Pilling also recommended updating supported equipment, isolating obsolete controllers and monitoring systems for unexpected changes.
“无论最终由谁负责,法国制冷系统攻击都应成为零售商和关联基础设施运营者的警钟,”他说。
"Regardless of who is ultimately responsible, the French refrigeration attack should be a wake-up call for retailers and operators of connected infrastructure," he said.
他补充道,支持食品供应、安全和日常服务的系统如今已成为“网络战场”的一部分,需要相应地加以保护。
Systems supporting food supplies, safety and day-to-day services are now part of the "cyber battlefield" and need to be secured accordingly, he added.